 SakerCP
Client
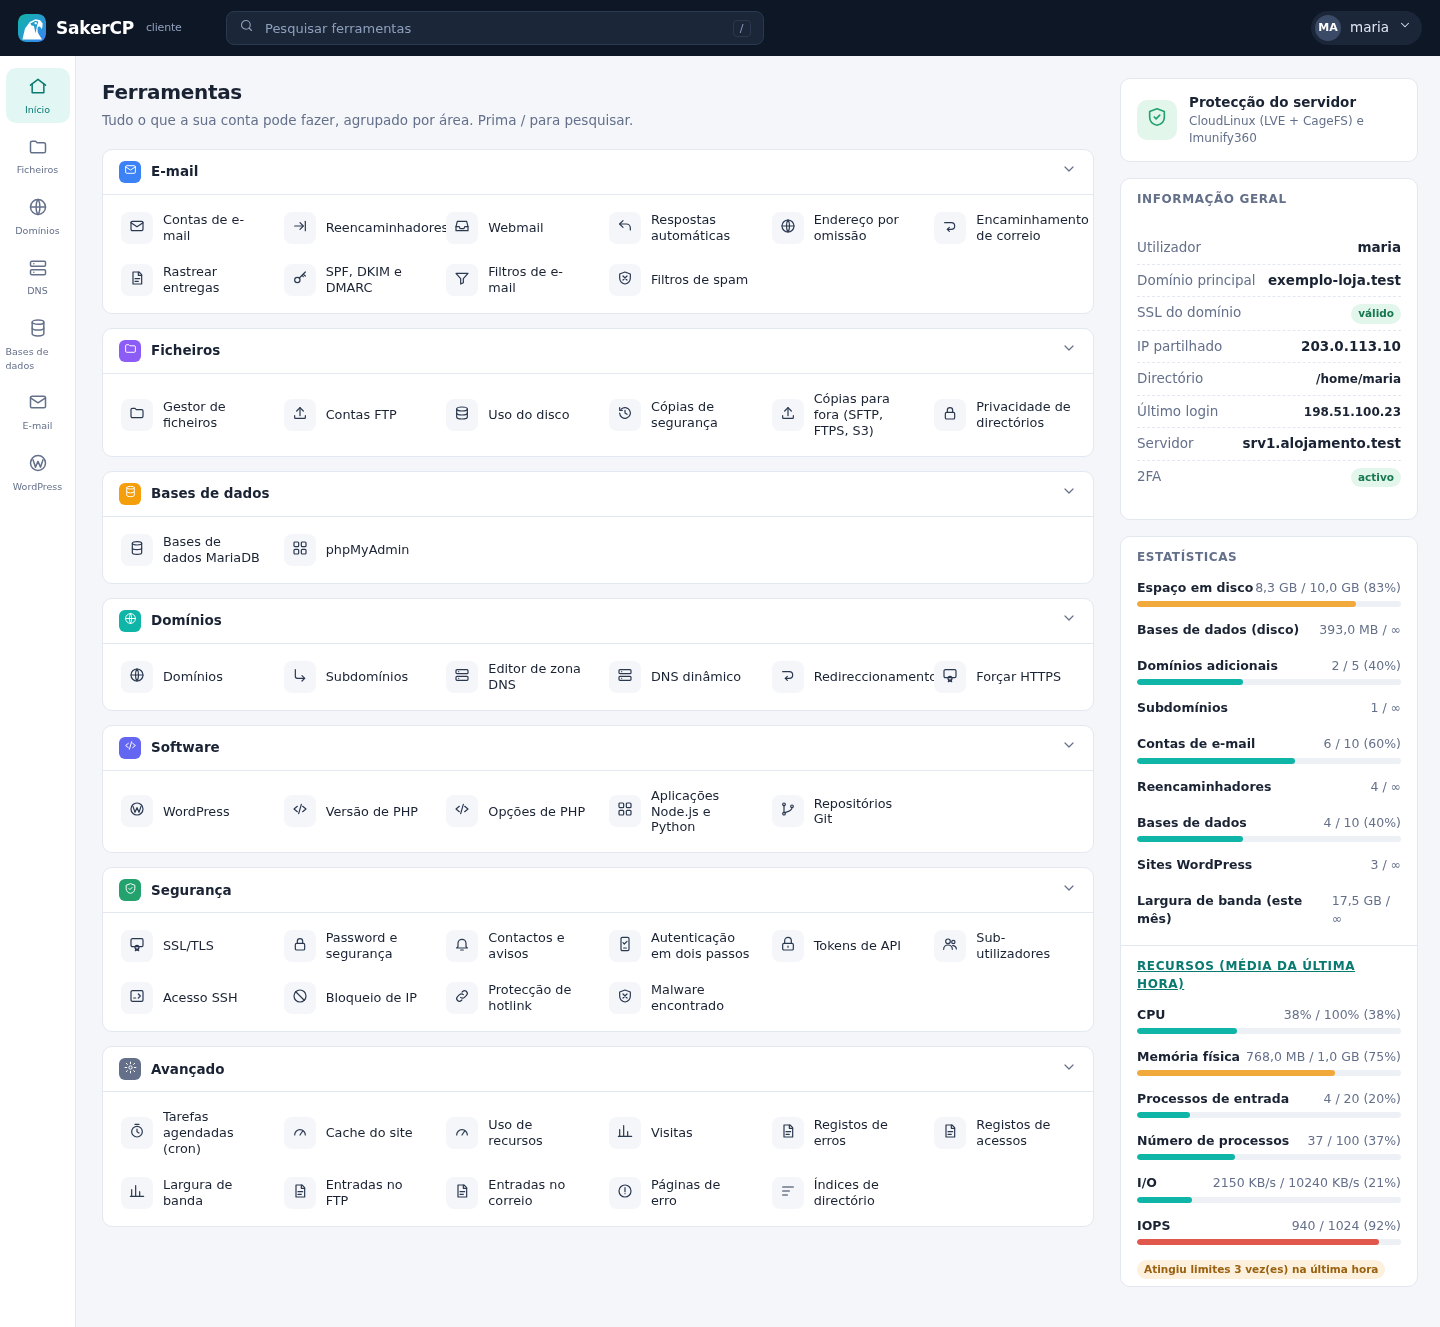
Mail with filters and anti-spam, domains and DNS, automatic certificates, file manager, databases, WordPress, Node.js and Python applications, Git, cron, key-only SSH, API tokens, sub-users and restoring backups by date.
Alpha · sign-ups open
Client, reseller and administration in one panel, written from scratch in Go for CloudLinux and Imunify360. The part that talks to the Internet has no power; the part that has power trusts no one.
Go, no shellCloudLinux · CageFS · LVEImunify360Security keys and passkeysPortuguese and EnglishSigned updates
Everything a client expects from a hosting panel, where they look for it, plus the tools of those who resell and those who run the server.
Mail with filters and anti-spam, domains and DNS, automatic certificates, file manager, databases, WordPress, Node.js and Python applications, Git, cron, key-only SSH, API tokens, sub-users and restoring backups by date.
Their own accounts and plans, with account and disk limits checked by the server, permissions granted one by one, private nameservers, dedicated IPs and logging into client accounts. They only see what they can use.
Accounts, plans and resellers; server status; automatic updates with rollback; an advisor with one-click fixes; Imunify360, LVE Manager and MySQL Governor; audit log. Only from the management networks, always with two factors.
Every request goes through layers with different privileges. A bug in one of them is not enough to take the server: the next one is always missing.
mail() or exec in PHP, mail sent only with a login and with an hourly limit.SakerBackupServer is SakerCP's backup platform: a separate machine that pulls the backups from the servers. The hosting server never holds a key that can delete them.
Whoever keeps the backups is whoever fetches them. A compromised server cannot reach them.
Mail every hour, databases every two hours, accounts every day, with retention.
The client picks the date and what they want back; the administration recovers a whole machine.
SakerCP imports accounts from cPanel* servers: from a backup archive or straight from the source server, with a second pass for whatever changed in the meantime. Mail, domains, DNS, databases and certificates come along, and anything that could not come is listed in a report.
* cPanel is a trademark of its respective owners. SakerCP is an independent product, written from scratch, with no third-party code.
CageFS, LVE limits, PHP, Node.js and Python selectors, MySQL Governor and Imunify360 integrated, and the panel adapts to each server's CloudLinux edition.
We are choosing the first servers for the alpha. Tell us who you are and what you host; we reply by e-mail. After sending, you will get a message to confirm your address.